RevSpring Data Breach Class Action Lawsuit Investigation
Data breach law firm Abington Cole + Ellery is investigating potential legal claims related to the RevSpring data breach, which reportedly affected an UNKNOWN number of individuals and may have exposed NAME / ADDRESS / SSN / DOB / TELEPHONE / EMAIL.
JOIN THIS INVESTIGATION: If you are interested in potentially volunteering to serve as a class representative in a class action lawsuit against RevSpring, please submit your information to be considered:
You may also open the form here: RevSpring Data Breach Lawsuit Form. An attorney-client relationship is not formed by submitting information through this website.
RevSpring Data Breach: Key Facts
| Company: | RevSpring, Inc. |
|---|---|
| Location: | Nashville, Tennessee |
| Incident Type: | Unauthorized Access |
| Number Affected: | TOTAL NOT YET PUBLICLY CONFIRMED |
| Data Involved: | name, home address, email address, telephone number, date of birth, Social Security number, and location of service |
| Date Began: | May 15, 2026 |
| Date Discovered: | August 17, 2026 |
| Date Ended: | June 1, 2026 |
| Notice Date: | November 4, 2026 |
| Credit Monitoring: | Free Kroll Identity Monitoring |
| Status: | Class Action Lawsuit Investigation |
What happened in the RevSpring data breach?
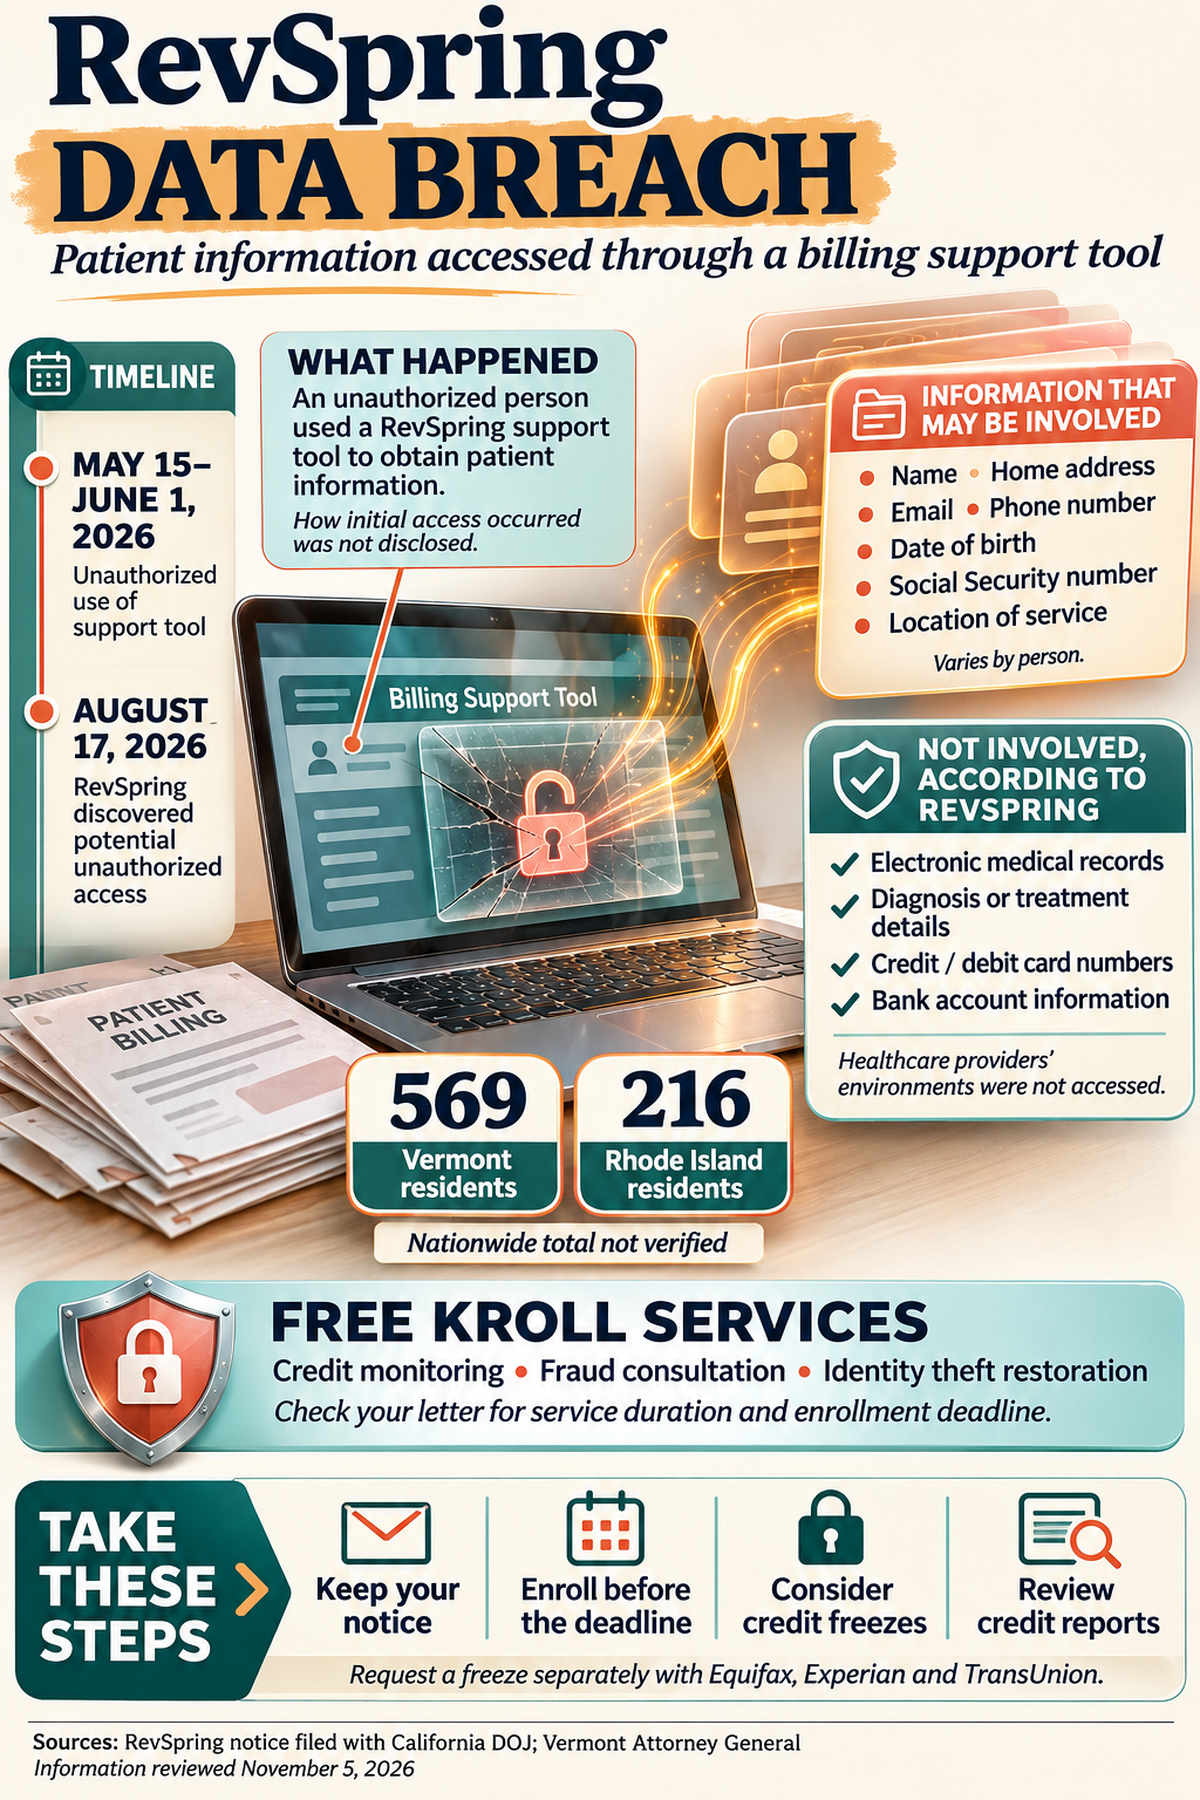
RevSpring, Inc. disclosed a data security incident involving information about patients who used its online bill payment platform through participating healthcare providers. According to the notification letter filed with the California Attorney General, an unauthorized person used a RevSpring support tool to obtain patient information between May 15 and June 1, 2026. RevSpring discovered the potential unauthorized access on August 17, 2026. Source: RevSpring California Submitted Breach Notification Sample
After discovering the issue, RevSpring launched an investigation, retained outside cybersecurity experts, and notified law enforcement. The investigation determined that the unauthorized person had successfully used the support tool to obtain information about patients of affected healthcare providers. The notice does not explain how that person initially gained access to the tool or identify a particular software vulnerability, stolen credential, or other entry point. Source: RevSpring California Submitted Breach Notification Sample
The information involved varies by person and may include names, home addresses, email addresses, telephone numbers, dates of birth, Social Security numbers, and locations of service. RevSpring states that the incident did not involve access to patients’ electronic medical records or the healthcare providers’ computer environments. The accessed information did not include diagnoses, treatment details, debit or credit card numbers, or bank account information. Source: RevSpring California Submitted Breach Notification Sample
RevSpring states that it implemented additional technical safeguards and other measures intended to reduce the likelihood of a similar incident. It is also offering affected recipients free identity monitoring through Kroll, including credit monitoring, fraud consultation, and identity theft restoration. The publicly available sample letter contains placeholders for the service duration and activation deadline, so recipients should consult their individual letters for those details. Source: RevSpring California Submitted Breach Notification Sample
The available records identify 569 affected Vermont residents and 216 affected Rhode Island residents. A nationwide total has not been verified, and the California filing reviewed does not state a California resident count. Sources: RevSpring California Submitted Breach Notification Sample; Vermont Security Breach Notices
How did the RevSpring data breach occur?
An unauthorized person used a RevSpring support tool to obtain information about patients who used its online bill payment platform. RevSpring has not publicly explained how the person gained access to that tool. The company states that the incident did not involve access to the healthcare providers’ environments or patients’ electronic medical records. Source: RevSpring California Submitted Breach Notification Sample
When did the RevSpring data breach occur?
The unauthorized person used the support tool between May 15 and June 1, 2026. RevSpring discovered the potential unauthorized access on August 17, 2026, more than two months after the identified activity ended. Source: RevSpring California Submitted Breach Notification Sample
How many people were affected by the RevSpring data breach?
A nationwide total has not been verified. Available disclosures identify 569 Vermont residents and 216 Rhode Island residents. The California filing confirms a notification concerning California residents but does not provide their number. Sources: RevSpring California Submitted Breach Notification Sample; Vermont Security Breach Notices
What information was exposed in the RevSpring data breach?
- Breached data reportedly may include, but is not necessarily limited to:
- Name
- Home address
- Social Security number
- Email address
- Telephone number
- Date of birth
- Location of service
Has RevSpring offered free credit monitoring and/or identity theft protection services?
Yes. RevSpring’s notice offers free Kroll identity monitoring, including single-bureau credit monitoring, fraud consultation, and identity theft restoration. The public sample does not specify the number of months or activation deadline because those fields are placeholders. Recipients should use the duration, deadline, activation code, and verification ID provided in their individual letters. Source: RevSpring California Submitted Breach Notification Sample
RevSpring Data Breach Timeline
| Date | Event |
|---|---|
| May 15, 2026 | Beginning of the period when an unauthorized person used a RevSpring support tool to obtain patient information. |
| June 1, 2026 | End of the unauthorized activity period identified in the notice. |
| August 17, 2026 | RevSpring discovered that an unauthorized person may have accessed the support tool. |
| Following discovery | RevSpring launched an investigation, engaged outside cybersecurity experts, and notified law enforcement. |
| Date not specified in the public sample | RevSpring informed the recipient’s healthcare provider. The sample letter leaves this date as a placeholder. |
| November 4, 2026 | RevSpring reported the breach to Vermont, identifying 569 affected residents. |
| Individual notice and enrollment dates | The public sample leaves the letter date, Kroll service duration, and activation deadline as placeholders. Sources: RevSpring California Submitted Breach Notification Sample; Vermont Security Breach Notices |
Who is RevSpring?
RevSpring, Inc. is a technology company headquartered in Nashville, Tennessee, that provides communication, data management, billing, and payment services. Its healthcare customers include hospitals, medical practices, health plans, and billing organizations. RevSpring’s services support patient intake, billing statements, online bill payment, and communications through mail, email, text messages, and telephone systems. The company also serves financial services businesses and other consumer markets. Source: RevSpring Website
What should you do if you received a RevSpring data breach letter?
-
- Read and retain your notification letter. Review the information involved and any healthcare provider identified in the letter. Keep the notice and enrollment instructions for reference. The public sample contains placeholders, so your personal letter is the source for your enrollment deadline and service duration. Source: RevSpring California Submitted Breach Notification Sample
- Enroll in the free Kroll services before your deadline. The notice directs recipients to Kroll’s enrollment website. Use the unique activation code and verification ID in your letter. The offered services include credit monitoring, fraud consultation, and help restoring your identity if identity theft occurs. Source: RevSpring California Submitted Breach Notification Sample
- Consider placing a free security freeze with all three credit bureaus. Contact Equifax, Experian, and TransUnion separately. A freeze restricts access to your credit report and makes it harder for someone to open new credit accounts in your name. You can temporarily lift it when you need to apply for credit. Source: FTC: Credit Freezes and Fraud Alerts
- Consider a fraud alert. An initial fraud alert tells lenders to verify your identity before opening new credit accounts. It is free and lasts one year. Contact one nationwide credit bureau; that bureau must notify the other two. Source: FTC: Credit Freezes and Fraud Alerts
- Review your credit reports and account statements. Obtain free credit reports through AnnualCreditReport.com and check for unfamiliar accounts or inquiries. RevSpring also recommends reviewing statements from healthcare providers and financial institutions and promptly reporting suspicious activity. Source: FTC: Checking Your Credit Report
- Watch for suspicious messages and calls. Verify unexpected requests concerning bills, breach assistance, or account verification before providing sensitive information. Use a website or telephone number independently known to be legitimate. Enable multifactor authentication on important accounts to help protect them from unauthorized access. Source: FTC: How To Recognize and Avoid Phishing Scams
- Report suspected identity theft promptly. Contact the fraud department of any business where unauthorized activity occurred and ask it to close or freeze fraudulent accounts. Visit IdentityTheft.gov to report identity theft and obtain a personalized recovery plan. Keep records of suspicious activity, communications, and steps taken to resolve the problem. Source: FTC Consumer Advice: Identity Theft
- Contact the incident assistance line if needed. RevSpring’s notice lists 844-971-8621, available Monday through Friday, 8:00 a.m. to 5:30 p.m. Central Time, excluding major U.S. holidays, for questions about the incident or help enrolling in Kroll services. Source: RevSpring California Submitted Breach Notification Sample
RevSpring Data Breach Notice
The notice describes the RevSpring data breach, including the type of information that may have been involved and the steps offered to affected individuals.
Open the RevSpring Data Breach Notice in a New Tab
Sources & Additional Information About the RevSpring Data Breach
-
- RevSpring Website
- RevSpring California Submitted Breach Notification Sample
- Vermont Security Breach Notices
- FTC: How To Recognize and Avoid Phishing Scams
- my Social Security
- Medicare.gov: Reporting Medicare fraud & abuse
- FTC: Checking Your Credit Report
- FTC: Credit Freezes and Fraud Alerts
- AnnualCreditReport.com
- FTC Consumer Advice: Identity Theft
- IdentityTheft.gov
- IRS Identity Theft Guide for Individuals
- IRS Identity Theft Guide Central
- IRS: Get an identity protection PIN (IP PIN)
- U.S. Department of Health and Human Services Office of Inspector General: Medical Identity Theft
- IdentityTheft.gov: What To Do if Your Information Was Lost or Stolen, or Part of a Data Breach
Class Action FAQ
About This Data Breach Resource
This page was created to give affected individuals and researchers a clear, comprehensive explanation of the RevSpring data breach. It summarizes what is currently known about the incident, including the timeline, how the breach was discovered, the types of information involved, the number of people affected when available, important notice dates, and steps individuals may want to take after receiving a data breach notification.
This resource is independently written and organized to help readers understand the breach without having to review multiple notices, state attorney general filings, company statements, and related materials. When available, this page relies on primary sources and identifies key facts, unanswered questions, and updates as new information becomes public.
This page is especially relevant for readers searching for information about the RevSpring data breach, RevSpring data breach notice, RevSpring class action investigation, what information was exposed, how many people were affected, and what affected individuals should do next.
Abington Cole + Ellery reviews data breach incidents involving sensitive personal information, financial information, and protected health information. This page is intended to help affected individuals understand the publicly reported facts, the types of information that may have been involved, and practical steps that may reduce the risk of identity theft or medical identity theft.
The information on this webpage is provided for general informational purposes only and does not constitute legal advice. Nothing on this page should be relied upon as legal advice for any particular situation. Submitting information through this page does not create an attorney-client relationship.
For more information about steps you can take to possibly reduce the risk harm arising from a data breach, please review the following article: What are some steps you can take if you've been the victim of a data breach?
This website is not associated with nor authorized by RevSpring or any affiliated companies. If you have received any other data breach notifications, you may want to review Abington Cole + Ellery's current list of data breach investigations.