MedImpact Healthcare Systems Data Breach Class Action Lawsuit Investigation
Data breach law firm Abington Cole + Ellery is investigating potential legal claims related to the MedImpact Healthcare Systems data breach, which reportedly affected about 327,082 individuals and may have exposed names, addresses, dates of birth, subscriber numbers, Social Security numbers, health insurance information, and health-related details.
JOIN THIS INVESTIGATION: If you are interested in potentially volunteering to serve as a class representative in a class action lawsuit against MedImpact Healthcare Systems, please submit your information to be considered:
You may also open the form here: MedImpact Healthcare Systems Data Breach Lawsuit Form. An attorney-client relationship is not formed by submitting information through this website.
MedImpact Healthcare Systems Data Breach: Key Facts
| Company: | MedImpact Healthcare Systems |
|---|---|
| Location: | San Diego, California |
| Incident Type: | Ransomeware Attack |
| Number Affected: | APPROXIMATELY 327,082 |
| Data Involved: | names, addresses, dates of birth, subscriber numbers, Social Security numbers, health insurance information, and health-related details |
| Date Began: | October 18, 2025 |
| Date Discovered: | October 18, 2025 |
| Date Ended: | October 30, 2025 |
| Notice Date: | September 23, 2026 |
| Credit Monitoring: | Kroll single-bureau credit monitoring for some affected individuals |
| Status: | Class Action Lawsuit Investigation |
What happened in the MedImpact Healthcare Systems data breach?
MedImpact Healthcare Systems, Inc. disclosed a data breach involving personal and health-related information maintained in connection with its pharmacy benefit management services. According to the company’s notification filed with the California Attorney General, MedImpact identified unauthorized activity in certain systems on October 18, 2025. It secured the affected systems and engaged cybersecurity specialists to investigate. A subsequent review determined that information belonging to certain health plan members was included in the potentially affected data. October 18 is the confirmed detection date; the notice does not establish when the unauthorized access first began or how long it continued. California Submitted Breach Notification Sample, MEDIMPACT STATEMENT REGARDING CYBERSECURITY INCIDENT
The publicly available notice provides limited information about how the MedImpact data breach occurred. It does not identify the attacker’s entry point, a particular software vulnerability, or whether compromised credentials were involved. Separately, HIPAA Journal reported that a ransomware group claimed responsibility in October 2025, alleging that it had stolen sensitive information and threatening to publish it unless a ransom was paid. That attribution remains a reported claim by the threat group; MedImpact’s California notice does not confirm involvement of a ransomware group, the deployment of ransomware, or a ransom payment. HIPAA Journal: Data Breaches Announced by MedImpact Healthcare Systems
The investigation and notification process extended into 2026. HIPAA Journal reported that MedImpact finalized its investigation on July 17, 2026, informed affected clients on August 13, 2026, and began mailing individual notification letters on behalf of affected clients on September 23, 2026. A separate September 16 update from the Joint Health Management Board, which serves Fresno Unified health plan members, confirmed that MedImpact notified it in August after reviewing the potentially affected data. California’s breach database lists MedImpact’s filing date as September 25, 2026. These dates represent different stages of the response and should be distinguished from the October 2025 detection date. JHMB: Important Update About the MedImpact Cybersecurity Incident
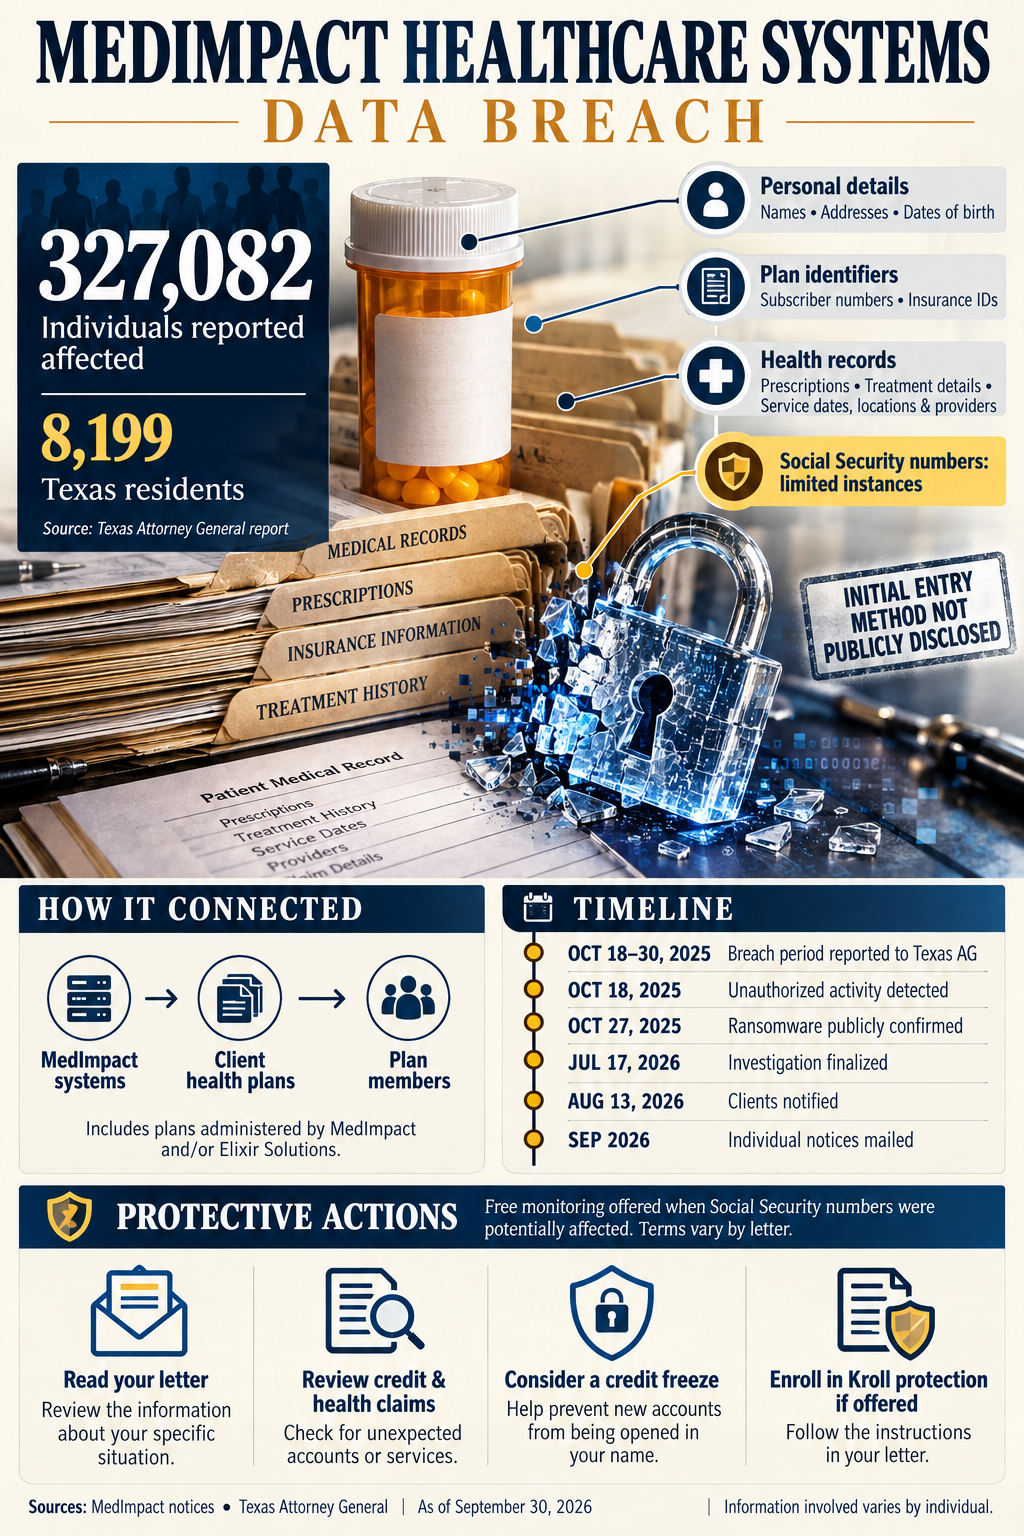
The information potentially affected varied by individual. Reported data categories included names, addresses, dates of birth, subscriber numbers, Social Security numbers, health insurance information, and health-related details. Those health-related records could include prescription and treatment information, dates of service, service locations, and provider names. The public California sample letter uses a placeholder for each recipient’s specific data elements, so it does not establish that every listed category was involved for every person. Individual notification letters should identify the information associated with each recipient. California Submitted Breach Notification Sample
The incident also affected information MedImpact handled for client benefit plans. For example, the Leggett & Platt, Incorporated Employee Benefits Plan submitted notices concerning the MedImpact incident to California on September 15, 2026. The Joint Health Management Board’s update likewise identified potentially affected current and former members of its PPO Plan A and Plan B and stated that the incident occurred within MedImpact’s environment. These disclosures show how a breach at a pharmacy benefit manager can involve members of separate health plans that use its services. JHMB: Important Update About the MedImpact Cybersecurity Incident
MedImpact stated that it enhanced security safeguards and monitoring following the incident and had no reason to believe the affected information had been or would be misused. It arranged complimentary Kroll identity protection services for eligible recipients, including credit monitoring, fraud consultation, and identity theft restoration. Monitoring eligibility varies, and the public sample notice leaves the service duration and enrollment deadline unspecified. Recipients should therefore consult their own letters for those details. MedImpact’s notice lists 844-958-8925, available Monday through Friday from 8 a.m. to 5:30 p.m. Central Time, for questions about the incident. California Submitted Breach Notification Sample
How did the MedImpact Healthcare Systems data breach occur?
The MedImpact Healthcare Systems breach involved unauthorized access to its systems and a likely ransomware incident, but the attacker’s initial method of entry has not been publicly disclosed. MEDIMPACT STATEMENT REGARDING CYBERSECURITY INCIDENT
When did the MedImpact Healthcare Systems data breach occur?
According to the Texas Attorney General’s breach report, the MedImpact Healthcare Systems data breach occurred between October 18 and October 30, 2025. MedImpact detected unauthorized activity on October 18, 2025. Texas Attorney General Data Security Breach Reports
How many people were affected by the MedImpact Healthcare Systems data breach?
MedImpact Healthcare Systems reported that the data breach affected 327,082 individuals, including 8,199 Texas residents, according to data published by the Texas Attorney General’s Office.
What information was exposed in the MedImpact Healthcare Systems data breach?
- According to MedImpact’s breach notice, the potentially exposed information varied by individual and included:
- First and last names
- addresses
- Dates of birth
- Subscriber numbers
- Health insurance identification numbers
- Prescription information
- Treatment information, including dates of service, treatment locations, and provider names
- Social Security numbers, in limited instances
Has MedImpact Healthcare Systems offered free credit monitoring and/or identity theft protection services?
Yes. MedImpact offered complimentary credit monitoring and identity theft protection to individuals whose Social Security numbers were potentially affected. The monitoring duration and enrollment deadline are specified in each eligible recipient’s notification letter. The public sample leaves those details as placeholders, so it does not establish a universal coverage period. Questions can be directed to 844-958-8925, Monday–Friday, 8 a.m.–5:30 p.m. Central Time, excluding major U.S. holidays.
MedImpact Healthcare Systems Data Breach Timeline
| Date | Event |
|---|---|
| October 18, 2025 | MedImpact detected unauthorized activity within certain systems and began securing them and investigating with outside cybersecurity experts. |
| October 18–30, 2025 | Breach period listed in the Texas Attorney General’s underlying report data. |
| October 27, 2025 | MedImpact publicly confirmed ransomware on certain systems. It reported restoring affected systems in a separate environment and said pharmacy claims were processing for all clients. |
| July 17, 2026 | MedImpact finalized its investigation and determined that information belonging to certain individuals was included in the potentially affected data. |
| August 13, 2026 | MedImpact notified affected clients of the incident. |
| September 23, 2026 | MedImpact began mailing notification letters to potentially affected individuals on behalf of its clients. |
Who is MedImpact Healthcare Systems?
MedImpact Healthcare Systems, Inc. is a pharmacy benefit management company headquartered in San Diego, California. Founded in 1989, it administers prescription drug benefits for commercial health plans, self-insured employers, and government programs, including Medicare Part D and Medicaid plans. Its services include pharmacy benefit administration, clinical support, data analytics, and tools that help members review medication coverage, prescription costs, and participating pharmacies. MedImpact operates as an intermediary in the prescription benefits system, supporting the organizations that provide drug coverage and the individuals enrolled in their plans. MedImpact Healthcare Systems Website
What should you do if you received a MedImpact Healthcare Systems data breach letter?
If you received a MedImpact Healthcare Systems data breach letter, take these steps:
-
- Read and save the letter. Identify which information was potentially exposed, particularly whether your Social Security number was involved. Keep the notice and records of any related expenses or suspicious activity.
- Enroll in free protection if offered. MedImpact offers complimentary credit monitoring and identity theft protection to individuals whose Social Security numbers were potentially affected. Follow your letter’s enrollment instructions and activation deadline.
- Consider freezing your credit. A free freeze at Equifax, Experian, and TransUnion makes it harder for someone to open credit accounts in your name. You must contact each bureau separately. Credit monitoring alerts you to changes; a freeze restricts access to your credit report. FTC: Credit Freezes and Fraud Alerts
- Review financial and healthcare records. Check credit reports, account statements, prescription claims, medical bills, and insurance explanations of benefits for unfamiliar activity. Report questionable healthcare claims to your insurer or provider. MedImpact specifically recommends reviewing health insurance claims and monitoring financial records.
- Watch for targeted scams. Treat unexpected calls, emails, or texts requesting personal information with caution—even if the sender knows your health plan or prescription details. Verify requests through contact information you already trust.
- Report identity theft promptly. If you discover misuse, visit IdentityTheft.gov for a recovery plan and contact the affected financial institution, insurer, or healthcare provider.
For questions about your letter or monitoring eligibility, call MedImpact’s incident assistance line at 844-958-8925, Monday–Friday, 8 a.m.–5:30 p.m. Central Time, excluding major holidays.
MedImpact Healthcare Systems Data Breach Notice
The notice describes the MedImpact Healthcare Systems data breach, including the type of information that may have been involved and the steps offered to affected individuals.
Open the MedImpact Healthcare Systems Data Breach Notice in a New Tab
Sources & Additional Information About the MedImpact Healthcare Systems Data Breach
-
- MedImpact Healthcare Systems Website
- California Submitted Breach Notification Sample
- HIPAA Journal: Data Breaches Announced by MedImpact Healthcare Systems
- JHMB: Important Update About the MedImpact Cybersecurity Incident
- Texas Attorney General Data Security Breach Reports
- MEDIMPACT STATEMENT REGARDING CYBERSECURITY INCIDENT
- my Social Security
- Medicare.gov: Reporting Medicare fraud & abuse
- FTC: Checking Your Credit Report
- FTC: Credit Freezes and Fraud Alerts
- AnnualCreditReport.com
- FTC Consumer Advice: Identity Theft
- IdentityTheft.gov
- IRS Identity Theft Guide for Individuals
- IRS Identity Theft Guide Central
- IRS: Get an identity protection PIN (IP PIN)
- U.S. Department of Health and Human Services Office of Inspector General: Medical Identity Theft
- IdentityTheft.gov: What To Do if Your Information Was Lost or Stolen, or Part of a Data Breach
Class Action FAQ
About This Data Breach Resource
This page was created to give affected individuals and researchers a clear, comprehensive explanation of the MedImpact Healthcare Systems data breach. It summarizes what is currently known about the incident, including the timeline, how the breach was discovered, the types of information involved, the number of people affected when available, important notice dates, and steps individuals may want to take after receiving a data breach notification.
This resource is independently written and organized to help readers understand the breach without having to review multiple notices, state attorney general filings, company statements, and related materials. When available, this page relies on primary sources and identifies key facts, unanswered questions, and updates as new information becomes public.
This page is especially relevant for readers searching for information about the MedImpact Healthcare Systems data breach, MedImpact Healthcare Systems data breach notice, MedImpact Healthcare Systems class action investigation, what information was exposed, how many people were affected, and what affected individuals should do next.
Abington Cole + Ellery reviews data breach incidents involving sensitive personal information, financial information, and protected health information. This page is intended to help affected individuals understand the publicly reported facts, the types of information that may have been involved, and practical steps that may reduce the risk of identity theft or medical identity theft.
The information on this webpage is provided for general informational purposes only and does not constitute legal advice. Nothing on this page should be relied upon as legal advice for any particular situation. Submitting information through this page does not create an attorney-client relationship.
For more information about steps you can take to possibly reduce the risk harm arising from a data breach, please review the following article: What are some steps you can take if you've been the victim of a data breach?
This website is not associated with nor authorized by MedImpact Healthcare Systems or any affiliated companies. If you have received any other data breach notifications, you may want to review Abington Cole + Ellery's current list of data breach investigations.